
and Compliantly in Your Dealership
In today's automotive industry, a dealership's most valuable asset is not just the inventory on the lot, but the trust of its customers. A critical component of earning and maintaining that trust is the responsible management of sensitive personal information. Storing customer records securely and compliantly is no longer an option, it is a legal and ethical necessity. From credit applications and driver's license copies to financing agreements and contact details, every piece of data must be protected against unauthorized access and potential breaches. Adhering to federal and state regulations, like the FTC Safeguards Rule, not only protects your customers from identity theft but also shields your business from significant financial penalties and reputational damage. A robust data security strategy demonstrates a commitment to professionalism and integrity, building a foundation of confidence that turns first-time buyers into lifelong clients. It is a cornerstone of a modern, successful dealership.
Implementing a comprehensive plan for storing customer records is an investment in your dealership's future. By prioritizing data protection, you actively reduce risk and enhance operational efficiency. A clear, compliant system ensures that your team handles information consistently and correctly, minimizing the chance of human error. This commitment to security becomes a powerful selling point, reassuring customers that they are dealing with a reputable and trustworthy business. Ultimately, a strong compliance posture strengthens your brand and fosters lasting customer relationships, which are essential for long-term growth and success.
A Dealer's Comprehensive Guide to Data Security and Compliance
For any modern used car dealership, managing customer information extends far beyond simple filing. The process involves a complex web of legal requirements, technological safeguards, and procedural diligence. Failure to properly handle this sensitive data can lead to disastrous consequences, including steep fines, legal action, and a complete erosion of customer trust. This guide delves into the essential practices and regulatory frameworks every dealership must understand to store customer records securely and maintain full compliance.
Navigating the Regulatory Landscape
Several key federal regulations govern how dealerships must handle consumer information. Understanding these rules is the first step toward building a compliant data management system. Ignoring them is not an option and can result in severe penalties.
The most significant of these is the Federal Trade Commission's (FTC) Standards for Safeguarding Customer Information, commonly known as the Safeguards Rule. This rule requires all financial institutions, including auto dealerships that extend credit, to develop, implement, and maintain a comprehensive security program to protect customer information. For a deeper dive, explore how the FTC Safeguards Rule applies to dealerships. A core component of this rule is the creation of a Written Information Security Plan (WISP), which outlines your dealership's specific policies and procedures for protecting data.
Another critical piece of legislation is the Red Flags Rule. This rule mandates the development and implementation of a written Identity Theft Prevention Program. Your program must be designed to detect, prevent, and mitigate identity theft in connection with the opening of a new account or any existing account. For dealerships, this applies directly to financing applications and vehicle sales. You can learn more about Red Flags Rule compliance to ensure your processes are sound.
Key Types of Customer Data to Protect
To secure customer data effectively, you must first identify what constitutes sensitive information. This is often referred to as Personally Identifiable Information (PII). Any data that could be used to distinguish or trace an individual's identity is PII and requires stringent protection. For a dealership, this includes a wide range of documents and data points.
- Full legal names and home addresses.
- Social Security numbers.
- Driver’s license numbers and state-issued ID information.
- Credit history, credit scores, and detailed financial statements.
- Bank account numbers and credit or debit card numbers.
- Employment history and income verification documents like pay stubs.
This information can exist in both physical and digital formats, and both require their own specific security protocols. The way you handle a paper credit application should be just as secure as how you store a scanned copy in your Dealer Management System (DMS).
Best Practices for Physical and Digital Security
A comprehensive security strategy addresses both paper records and electronic data. One cannot be prioritized over the other, as a weakness in either can lead to a breach.
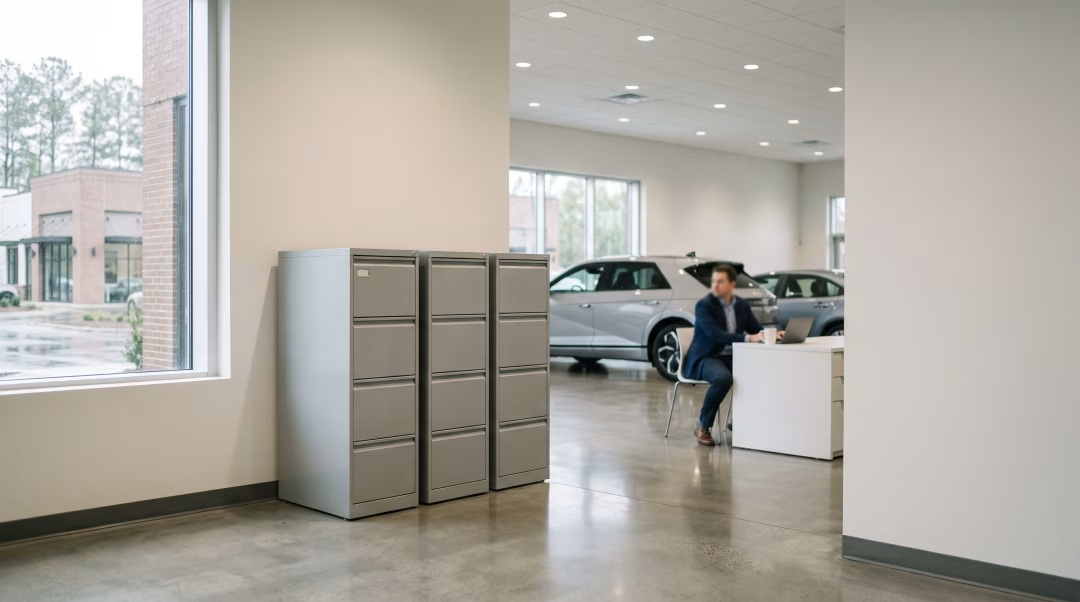
For physical records, such as printed applications, signed contracts, and photocopied IDs, strict access controls are paramount. All documents containing PII should be stored in locked, fire-resistant filing cabinets or in a secure room with limited access. Implement a "clean desk" policy, ensuring that sensitive documents are not left unattended on desks, printers, or in common areas. When documents are no longer needed, they must be destroyed using a commercial-grade cross-cut shredder or a certified document destruction service. Simply throwing them in the trash is a major compliance violation.
Digital security requires a multi-layered approach. All computer systems storing customer data must be protected with strong, unique passwords and multi-factor authentication (MFA) whenever possible. Data should be encrypted both "at rest" (when stored on a server or hard drive) and "in transit" (when sent via email or over the internet). Your dealership's network should be secured with a robust firewall, and your Wi-Fi network must be password-protected and encrypted. The move toward going paperless with document management can centralize security, but it also increases the importance of digital safeguards. Your Dealer Management System (DMS) is the heart of your digital operations, so ensure it has strong, built-in security features and access controls based on employee roles.
The Importance of Employee Training and Policies
Your employees are the first line of defense against a data breach. Technology and policies are only effective if the people using them are well-informed and diligent. Regular, ongoing training on compliance basics and data security is non-negotiable. This training should cover:
- How to identify and handle PII.
- The dealership's specific policies for physical and digital security.
- Recognizing and reporting phishing attempts and other forms of social engineering.
- Proper procedures for document retention and destruction.
- The dealership’s incident response plan in the event of a suspected breach.
Alongside training, you must establish clear record-keeping standards and a formal document retention policy. This policy should define how long different types of records must be kept to meet legal and operational needs, as well as the procedures for their secure disposal once they are no longer required. Storing data indefinitely creates unnecessary risk. By systematically purging old records, you minimize your data footprint and reduce the potential impact of a breach. When it is time for an audit, being prepared is key. For more information, read about how to prepare for a state compliance audit to ensure your dealership is ready.
What is the FTC Safeguards Rule and why does it apply to car dealerships?
The FTC Safeguards Rule requires financial institutions to have a security plan to protect the confidentiality and security of customer information. Because most car dealerships offer financing or leasing, they are considered financial institutions under this rule. The rule mandates that dealerships develop a written information security plan, conduct risk assessments, and implement safeguards to control risks to customer data.
How long should our dealership keep customer records on file?
The required retention period for customer records varies based on the type of document and applicable federal and state laws. For example, documents related to a credit transaction under the Equal Credit Opportunity Act must generally be kept for 25 months. It is essential to create a formal document retention policy, developed with legal counsel, that outlines the specific timeframes for all types of records your dealership handles.
What is the biggest security risk for a dealership's customer data?
While technology threats like malware are significant, the human element is often the biggest risk. Untrained employees are more susceptible to phishing scams, social engineering, or accidental mishandling of sensitive documents. This is why comprehensive and continuous employee training on data security protocols, privacy policies, and threat recognition is one of the most effective safeguards a dealership can implement.
What is PII in the context of a car dealership?
PII, or Personally Identifiable Information, is any data that can be used to identify a specific individual. At a dealership, this includes non-public information like a customer's Social Security number, driver's license number, financial history from a credit report, bank account details, and even their home address and date of birth when combined with their name. All of this information must be protected under privacy regulations.
Is cloud storage a secure option for our dealership's documents?
Cloud storage can be a very secure option, provided you choose a reputable vendor that offers robust security features. Key features to look for include end-to-end encryption, multi-factor authentication, detailed access logs, and compliance with standards like SOC 2. Using a secure, professionally managed cloud platform is often safer than maintaining an on-site server, as it provides expert security management and data redundancy.
